


DevOps & DevSecOps: What's the difference?



DevOps has changed how teams build, test, and deliver software by bringing development and operations closer through automation and continuous delivery. As security becomes a greater part of the software development lifecycle, DevSecOps extends this approach by bringing security into the same workflow.
While both approaches aim to improve software delivery, their priorities and processes differ. DevOps focuses on collaboration, automation, and efficient delivery, while DevSecOps integrates security throughout the development and delivery lifecycle.
What Is the Difference Between DevOps and DevSecOps?
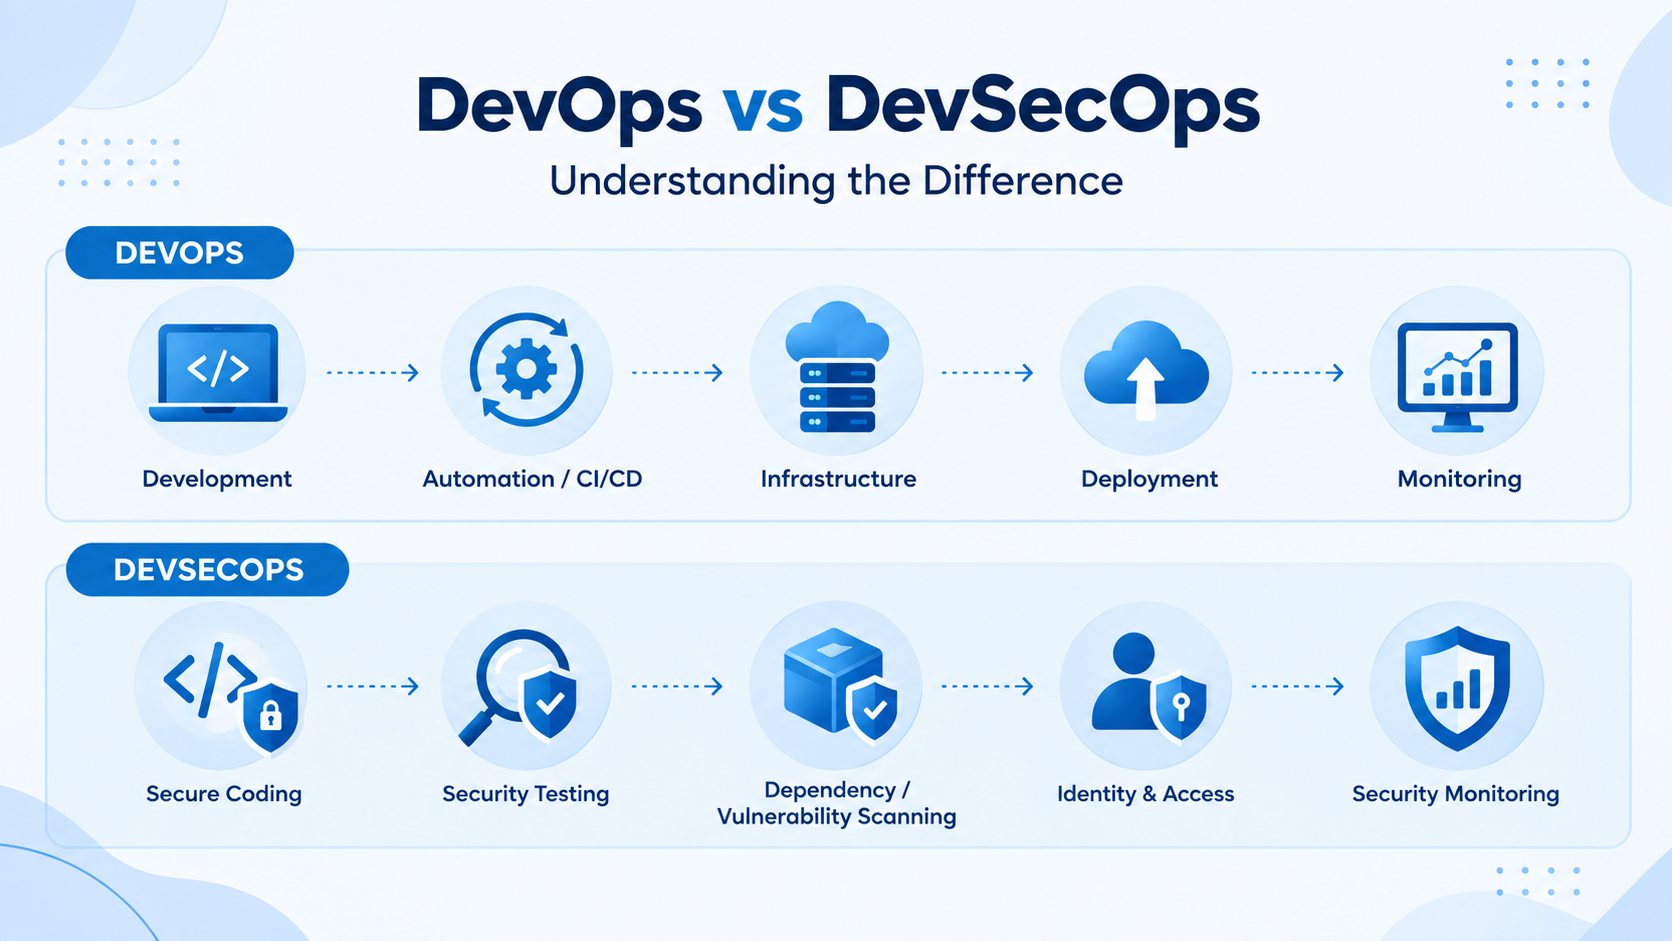
DevOps and DevSecOps follow similar principles of collaboration, automation, and continuous software delivery, but they differ in how security is incorporated into the development lifecycle. DevOps brings development and operations together to streamline software delivery, while DevSecOps extends these practices by making security a shared and continuous part of the process.
The key differences can be seen across their focus, team responsibilities, security practices, testing, automation, and monitoring.
In simple terms, DevOps connects development and operations to improve software delivery, while DevSecOps adds security as an integral part of that process. The difference is less about replacing one approach with another and more about expanding the development lifecycle to include security at every stage.
In DevSecOps, security is built into every stage of the development lifecycle, from planning and coding to testing, deployment, and monitoring. This helps teams identify vulnerabilities earlier, address security risks as part of regular development work, and reduce the chances of security issues being discovered only after deployment.
What is DevOps?
DevOps is a way of building and delivering software that brings together the people who write code and the people who run it. DevOps improves teamwork, makes many steps automatic, and speeds up delivery while keeping software reliable. Rather than treating writing, testing, deployment, and running as separate jobs, DevOps links them by using shared steps, automatic flows, and constant feedback.
DevOps focuses on giving software to users often and with confidence. DevOps cuts down on effort and makes the process steady from start to finish.
How Does DevOps Work?
DevOps links each step of building software with a process:
Plan → Code → Build → Test → Release → Deploy → Operate → Monitor
What Are the Key Features of DevOps?
Continuous Integration and Continuous Delivery
DevOps uses CI/CD practices to automate the movement of code from development through testing and deployment. Developers can regularly integrate code into a shared repository, where automated builds and tests help identify issues early.
Validated changes can then move through controlled release and deployment workflows.
Automation
Automation is a core part of DevOps, covering repetitive activities such as code builds, testing, deployments, infrastructure provisioning, and configuration management.
By reducing manual steps, teams can follow consistent processes and spend more time on development and problem-solving rather than repetitive operational tasks.
Infrastructure as Code
Infrastructure as Code allows teams to define and manage infrastructure through code instead of configuring environments manually.
Infrastructure configurations can be version-controlled, reviewed, updated, and reused, helping teams create more consistent development, testing, and production environments.
Collaboration Between Development and Operations
DevOps brings development and operations teams into a shared workflow instead of treating them as separate functions.
Both teams collaborate on areas such as development, testing, deployment, infrastructure, monitoring, and troubleshooting, creating clearer ownership across the software delivery lifecycle.
Continuous Testing and Monitoring
DevOps incorporates testing and monitoring throughout the software delivery process. Automated tests can validate application functionality and performance during development, while monitoring tools track application availability, errors, resource usage, and infrastructure health after deployment.
The resulting feedback can then be used to improve future releases.
What Is DevSecOps?
DevSecOps is a software development and delivery approach that integrates security into the DevOps lifecycle. Instead of treating security as a separate stage after development, DevSecOps brings security practices into planning, coding, testing, deployment, and operations.
It combines development, security, and operations so that security becomes a shared responsibility across teams. Automated security testing, vulnerability checks, secure configurations, and continuous monitoring can be integrated into development and CI/CD workflows to identify and address security issues earlier.
The goal is to maintain the speed and automation of DevOps while making security a continuous part of the software delivery process.
How Does DevSecOps Work?
DevSecOps follows a continuous lifecycle where security activities are integrated into the same workflow as development and operations.
Plan → Code → Secure → Build → Test → Release → Deploy → Operate → Monitor → Feedback
What Are the Key Features of DevSecOps?
Security Integrated Into the Development Lifecycle
DevSecOps brings security into the entire software development lifecycle, starting from planning and coding and continuing through testing, deployment, and operations.
Instead of treating security as a separate activity before release, teams consider security requirements alongside functional and technical requirements throughout development.
Automated Security Testing
Security testing is incorporated into CI/CD pipelines so that vulnerabilities can be identified as code and application changes move through the development process.
Teams can use practices such as SAST, DAST, dependency scanning, container scanning, and vulnerability testing to detect security issues before applications reach production.
Secure CI/CD and Infrastructure
DevSecOps extends automation beyond application builds and deployments by including security checks for CI/CD pipelines, infrastructure, configurations, and deployment environments.
Infrastructure as Code can also be reviewed for insecure configurations, while security policies and access controls can be applied as part of automated workflows.
Shared Security Responsibility
Security is treated as a shared responsibility between development, security, and operations teams.
Developers contribute through secure coding and vulnerability remediation, security teams provide policies and risk guidance, and operations teams help maintain secure infrastructure, access controls, and production environments.
Continuous Security Monitoring and Vulnerability Management
DevSecOps continues security activities after an application has been deployed. Teams can monitor security events, vulnerabilities, access activity, configuration changes, and potential threats while maintaining application and infrastructure monitoring.
This allows newly identified risks to be tracked, prioritised, and addressed as part of ongoing development and operations.
What Are the Use Cases of DevOps and DevSecOps?
DevOps and DevSecOps can be used across software development and delivery environments. While both approaches support collaboration, automation, and continuous delivery, their use cases differ based on whether the primary focus is improving software delivery or integrating security throughout that process.
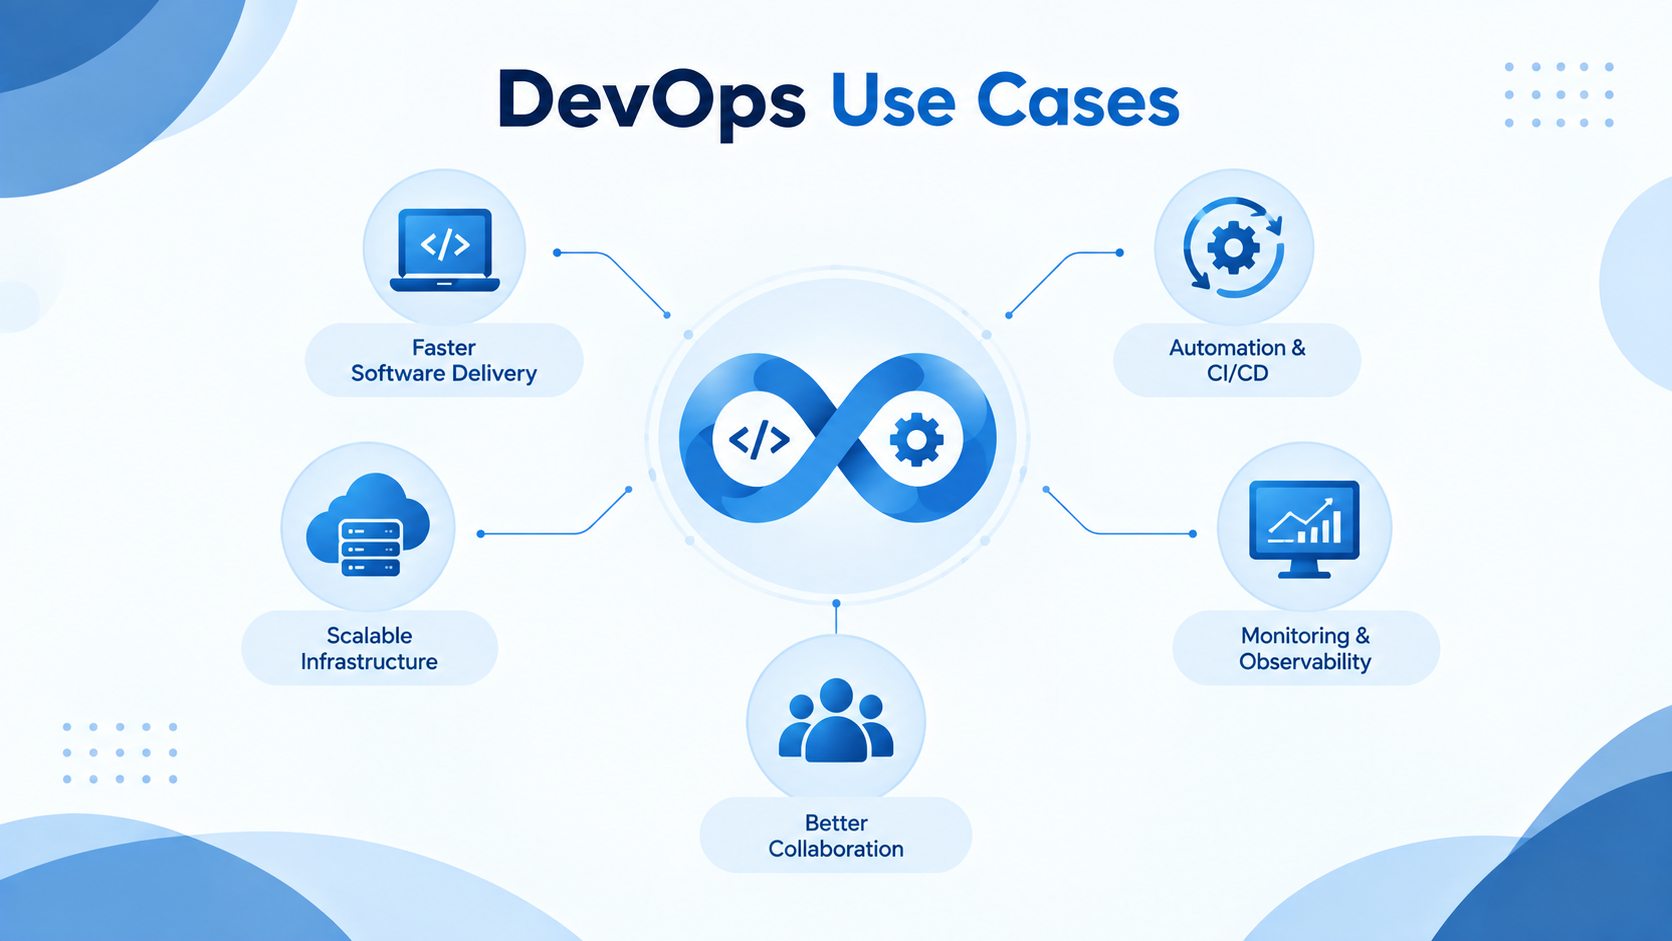
What Are the Common DevOps Use Cases?
1. Continuous Software Delivery
DevOps is commonly used by teams that need to build, test, and release software frequently. CI/CD pipelines can automate builds, testing, and deployments, helping teams move code through the development lifecycle with fewer manual steps.
This approach is useful for products that receive feature updates, bug fixes and improvements. Automated workflows can help development and operations teams maintain a release process while reducing delays between development and deployment.
2. Cloud Application Development
DevOps practices are widely used for developing and deploying applications in environments. Teams can combine deployments, Infrastructure as Code, configuration management, and monitoring to manage applications and their supporting infrastructure.
This allows development and operations teams to work with environments across development, testing and production. Cloud resources can also be. Updated through automated workflows rather than relying entirely on manual configuration.
3. Application Modernisation
Organisations modernising legacy applications can use DevOps to introduce practices such as automated testing, CI/CD, containerisation and Infrastructure as Code. These practices can support the migration of older development and deployment processes to modern workflows.
DevOps can also help teams manage changes during modernisation projects. Development and operations teams can collaborate closely while testing, deploying, and monitoring updated application components throughout the process.
4. Microservices and Distributed Applications
Microservices applications consist of services that may be developed, tested, deployed, and maintained independently. DevOps practices can help automate the build, testing, deployment, and monitoring processes for these services.
This is particularly useful when different teams are working on application components at the same time. Automated pipelines and monitoring help teams manage changes while maintaining visibility across the wider application environment.
5. Infrastructure Automation
DevOps is commonly used when organisations need to manage infrastructure across environments or cloud platforms. Infrastructure as Code allows infrastructure configurations to be defined through code, making provisioning and configuration management easier to automate and track.
Teams can use these practices to maintain consistent development, testing, and production environments. Changes to infrastructure can also be reviewed, version-controlled, and applied through established deployment workflows.
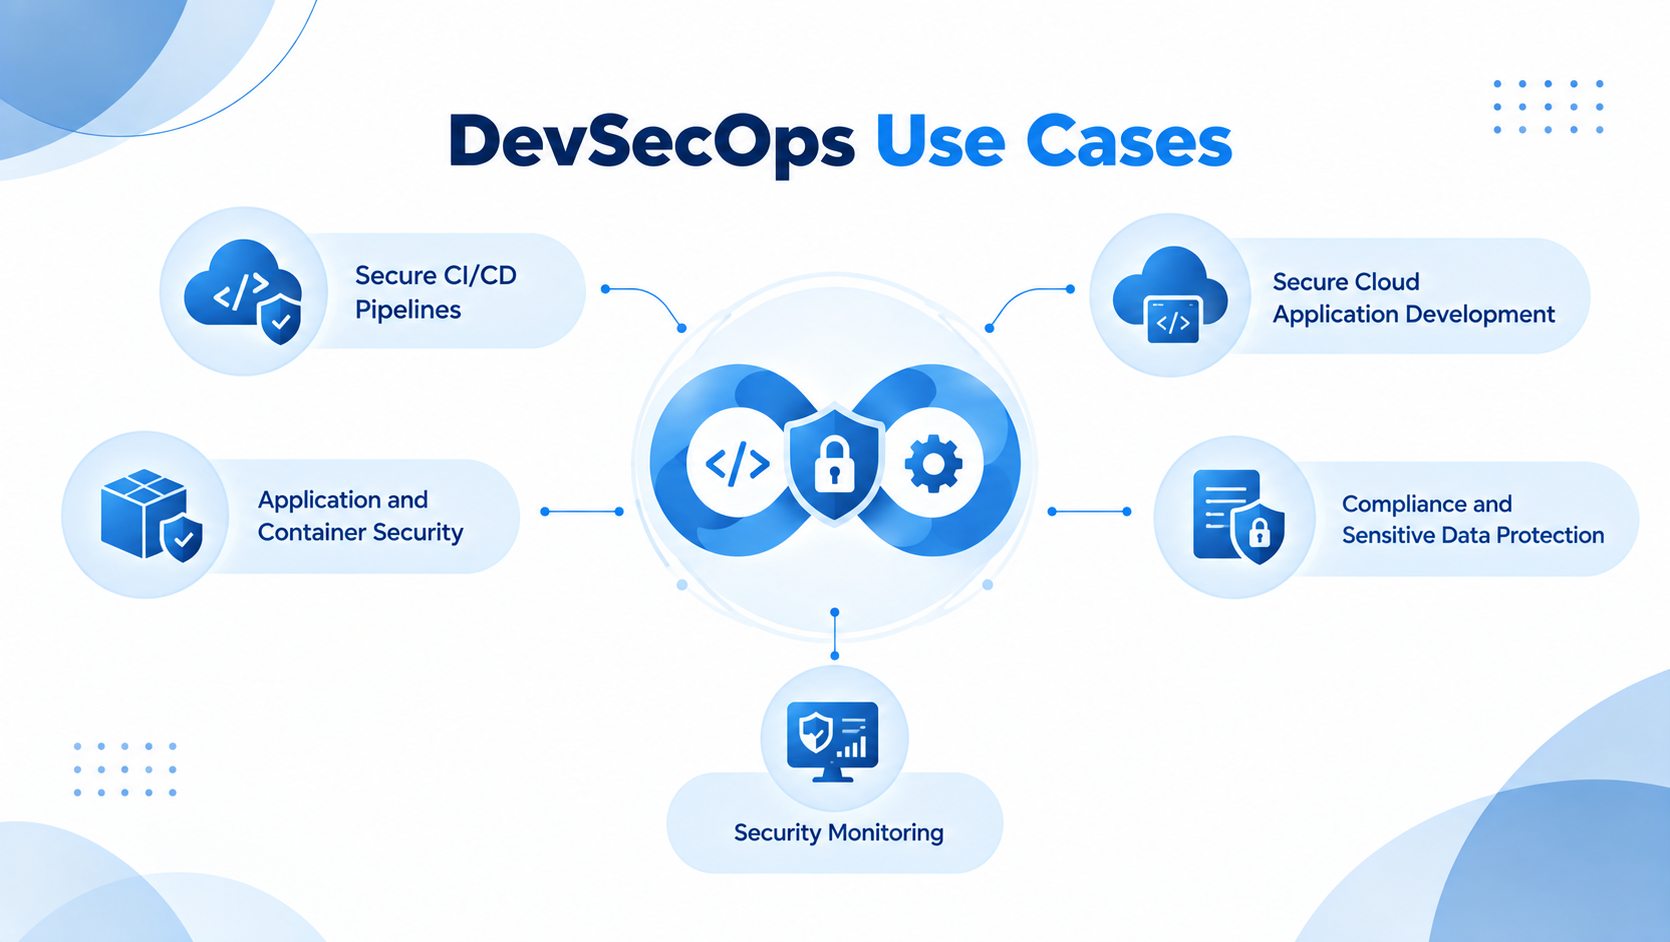
What Are the Common DevSecOps Use Cases?
1. Secure CI/CD Pipelines
DevSecOps is used when security needs to be incorporated into software delivery pipelines. Security checks such as code analysis, dependency scanning, vulnerability testing, and policy validation can be added alongside existing build and testing processes.
This allows security issues to be identified before applications reach later stages of the delivery process. Automated security checks can also reduce dependence on manual security reviews for every code or configuration change.
2. Secure Cloud Application Development
Cloud applications often involve services, APIs, databases, identities, and infrastructure components that need to be protected. DevSecOps integrates security checks into cloud development and deployment workflows to assess application code, dependencies, configurations, access controls, and cloud resources.
Security can therefore be considered alongside development and operational requirements throughout the application lifecycle. This approach is particularly useful when applications handle information or depend on multiple cloud services and third-party components.
3. Application and Container Security
Applications built using containers or microservices introduce security considerations across source code, dependencies, container images, workloads, and deployment configurations. DevSecOps can integrate vulnerability scanning, security testing, configuration checks, and access controls into development and deployment workflows.
Security checks can be performed as applications move through the CI/CD pipeline rather than waiting until deployment or production. This gives teams opportunities to identify vulnerabilities in application components and container environments earlier in the development process.
4. Compliance and Sensitive Data Protection
DevSecOps is useful for applications that handle information or operate under specific security and compliance requirements. Security policies, access controls, encryption, audit requirements, and automated checks can be incorporated into development and deployment workflows.
By integrating these controls into existing processes, teams can continuously check whether applications and infrastructure meet defined security requirements. This can also provide visibility into security-related changes across the development lifecycle.
5. Security Monitoring
Applications and cloud environments that require ongoing security visibility can use DevSecOps to combine security monitoring with regular operational monitoring. Teams can track security events, vulnerabilities, access activity, configuration changes, and potential threats, alongside application and infrastructure health.
This approach helps development, security, and operations teams respond to security findings as part of operations. Monitoring results can also provide feedback for development, testing, configuration, and security improvements.
When Should You Consider Moving From DevOps to DevSecOps?
Moving from DevOps to DevSecOps does not mean getting rid of the DevOps practices that are already in place. It means adding security practices to the development and delivery workflows that are already being used. The need for this change often becomes clearer as applications grow, as infrastructure changes, as development teams expand, and as security needs become more complicated.
Here are some situations where bringing in DevSecOps practices might make sense:
1. Security Problems Are Discovered Too Late
If problems with security are found during final testing, when the product is being reviewed for production, or after it is already running, then security is probably being added too late in the process. DevSecOps brings security checks earlier by using methods like scanning code, checking dependencies, and doing automated security tests.
Fixing problems earlier gives development teams time to look into them and fix them as part of their normal work. It stops security from becoming a task that only happens near the end of a release.
2. Security Checks Are Slowing Down New Releases
When security reviews are done mostly by hand at the end of the development process, they can slow down how often new versions are released. This can cause delays and extra work for development, operations, and security teams before an app can go live.
DevSecOps adds automated security checks into the integration and continuous delivery pipelines. This lets security tests run at the same time as development and testing. Manual reviews can still be used when needed. Routine checks become part of the regular delivery process.
3. Apps Deal With Protected Information
Apps that work with financial data, customer details, health information, company data or other private information usually need stronger security rules during development and deployment. As the type of data becomes more sensitive, security becomes more connected to how the app's built and how it runs.
DevSecOps adds access controls, encryption, vulnerability checking for vulnerabilities, security testing, monitoring, and checking for compliance into the software process. This helps teams handle security needs at the same time as they focus on other requirements.
4. Cloud Systems Are Getting More Complicated
As companies use more cloud services, containers, APIs, microservices, and infrastructure as code, the number of parts that need to be secured grows. Trying to handle security for infrastructure and deployment can make it hard to keep the same level of security across the board.
DevSecOps brings security into the cloud development and deployment process. Teams can check the security of configurations, identities, and other parts as part of the process that builds and delivers the app.
5. Teams Are Making Changes More Often
When development teams push out updates, often old security processes can be hard to keep up with. If every change needs a security check, it becomes difficult to keep everything running smoothly.
DevSecOps fixes this by automating security checks and making them part of the CI/CD pipeline. This lets teams check for security problems as code moves through the delivery process, doing it as a separate step before every release.
6. It Isn't Clear Who Is Responsible for Security
If security is handled by a separate team, developers and operations staff may not have much to do with finding or fixing security issues during the development process. This can lead to missed problems. Make it harder to include security in regular work.
DevSecOps makes security something that everyone takes part in. Development, security, and operations teams can work together on security needs, fixing problems, managing access, testing, watching for issues, and responding to security problems throughout the app’s life.
7. You Want Better Understanding of Security Risks
Traditional DevOps monitoring looks at how the app's performing, how the infrastructure is doing, how available the system is, and other operational issues. When companies want to track problems, like vulnerabilities, strange activity, access events, and other security threats, they may need insight.
DevSecOps adds security-focused monitoring and tracking. Security events and findings can be included in the work processes so the team gets a better overall picture of what is happening with the app, the infrastructure, and the security status.
How to Transition From DevOps to DevSecOps
Moving from DevOps to DevSecOps is about bringing security into the way a team already works. It does not mean starting over or replacing the existing DevOps setup. Instead, it means adding security steps into the current development and delivery processes.
This shift does not require doing everything at once. Teams can begin by building security checks into their CI/CD pipelines, improving how they handle access, managing vulnerabilities better, and monitoring for risks. The goal is to make security part of the flow of work.
A successful transition also depends on teamwork. Development, security, and operations teams must work together throughout the software lifecycle. Security should not be an afterthought handled at the end. It should be built in early. Keep it visible through every stage.
1. Assess the Existing DevOps Workflow
Start by looking at what the team already does. Review the development process,, the CI/CD pipeline, infrastructure setup, testing procedures, and deployment methods. See where security checks are already in place and identify any areas where security is missing or done late.
Look for places where vulnerabilities may go unnoticed, where configurations are risky, where access controls are weak, or where compliance issues are handled manually. This review gives a picture of where improvements are needed.
Understanding the setup helps avoid unnecessary changes. If something is working well there is no need to fix it. Only focus on the parts that need attention.
2. Define Security Requirements
Create a shared set of security rules that apply to applications, infrastructure, data, identities, and environments. These requirements should cover coding practices, identity and access control, how to handle vulnerabilities, encryption standards, dependency safety, and compliance needs.
It's important that all teams have development, security, and operations. Understand these requirements. When everyone knows what must be checked and maintained, it becomes easier to follow security practices consistently.
Clear requirements help prevent confusion. They give developers and operators a framework to follow when writing code, configuring systems or deploying apps.
3. Integrate Security Into CI/CD
Use the existing CI/CD pipeline to add automated security checks. Depending on the application, you can include code analysis scanning for vulnerable dependencies, checking container images, and other types of security tests.
These checks should run at key points in the pipeline. During code commits, builds, and before deployment. Running security scans early allows teams to catch problems before the code reaches production.
Automated security checks fit naturally into the workflow. They do not slow things down if done correctly. Instead, they help catch issues and build more secure software.
4. Secure Infrastructure and Configurations
Review infrastructure setups such as environments, servers, network settings and configuration files. Look for misconfigurations that could expose systems to risk. Also check Infrastructure as Code (IaC) scripts like Terraform or CloudFormation for weaknesses.
Pay attention to access permissions, network security groups, secrets storage and data handling settings. All of these play a role in keeping systems safe.
Security checks can be added to validate changes before they are applied. Automated tools can flag configurations and stop them from going live.
5. Introduce Vulnerability Management
Build an approach to finding and fixing vulnerabilities. This includes scanning code, open-source libraries, container images, infrastructure, and other components used in the software environment.
Instead of treating each vulnerability individually, set criteria for prioritising them. Consider factors like severity, exploitability, and impact on business operations. This makes it easier to decide which ones to fix first.
Vulnerability management should become an activity, not a one-time task. Tracking progress helps ensure nothing gets missed and reduces debt.
6. Strengthen Identity and Access Controls
Examine who has access to tools and resources. Including development platforms, cloud accounts, CI/CD pipelines, source repositories, applications, and production environments.
Apply authentication methods like multi-factor authentication and enforce least privilege access. That means users only get the permissions they absolutely need.
Regularly review access rights as teams grow applications. Infrastructure changes. Keeping access up to date helps reduce the chance of misuse or accidental exposure.
Access control should be managed as part of the DevSecOps process rather than treated separately.
7. Add Security Monitoring
Extend the monitoring systems in use to include security events. Track things like vulnerability alerts, unusual login attempts, configuration drift, suspicious behaviour, and failed access attempts.
Make sure these security signals feed into existing workflows. For example, alerts should go to the people using familiar tools and processes.
When security monitoring connects with operations, findings can be investigated quickly. This turns security insights into tasks that improve overall system resilience.
8. Build Security Into Team Responsibilities
DevSecOps means breaking down silos between development, security, and operations. Everyone shares responsibility for security rather than leaving it to a single team.
Developers need to learn coding patterns and participate in security testing. Operations teams should consider security when setting up infrastructure and managing deployments.
The security team supports this effort by creating policies offering guidance, running threat assessments, and providing tools. But they don’t own security alone. They help others do it right.
Team collaboration becomes essential. Regular meetings, shared dashboards, and joint ownership lead to outcomes.
9. Measure and Improve the Process
After implementing DevSecOps practices, evaluate how well they are working. Use metrics like the number of vulnerabilities found, the time it takes to fix them, test coverage, failed security checks, and recurring issues.
These numbers help track progress and show where improvements are needed. They also highlight whether security efforts are making a difference.
Treat the transition as a journey, not a final destination. Continuously refine your processes based on feedback and results. Over time, security becomes more effective and less disruptive.
The move from DevOps to DevSecOps is mainly about integrating security into an existing software delivery process. By reviewing workflows, defining clear security goals, securing CI/CD pipelines and infrastructure, managing vulnerabilities, improving access control, and adding security monitoring, teams can build security into everyday activities.
The key is to do it in a way that fits the existing DevOps style. There’s no need to overhaul everything. Start small, add value at every step, and grow security practices gradually.
With cooperation among development, security, and operations teams, security checks and controls can become a part of how software is planned, built, tested, deployed, and maintained.

Common DevOps vs DevSecOps Misconceptions
DevOps and DevSecOps share many practices, including collaboration, automation, CI/CD, infrastructure as code, testing, and monitoring. Because of this overlap, the two approaches are sometimes treated as completely separate methodologies or used as interchangeable terms. In practice, DevSecOps extends the DevOps approach by making security a continuous part of the software development and delivery lifecycle.
Understanding these differences helps teams choose and implement security practices based on their application, infrastructure, development process, and risk requirements.
1. DevSecOps Completely Replaces DevOps
Reality: DevSecOps does not replace DevOps or require teams to abandon their existing DevOps practices. DevOps provides the foundation through collaboration between development and operations, automation, CI/CD, Infrastructure as Code, continuous testing, and monitoring.
DevSecOps builds on this foundation by introducing security into the same workflows. Security testing, vulnerability management, access controls, secure configurations, and security monitoring can be integrated into existing development and deployment processes.
2. DevOps Does Not Include Security
Reality: Security can exist within a DevOps environment. Teams following DevOps practices may use security testing, access controls, vulnerability assessments, secure infrastructure configurations, and other security measures as part of their software delivery process.
The distinction is mainly in how security is incorporated into the lifecycle. DevSecOps places greater emphasis on integrating security earlier and continuously, making security checks part of development, CI/CD, infrastructure management, deployment, and operations rather than relying primarily on separate security activities.
3. DevSecOps Means the Security Team Is Responsible for Everything
Reality: DevSecOps is based on the idea of shared responsibility. Security teams continue to play an important role in defining security requirements, identifying risks, establishing policies, and supporting security testing, but developers and operations teams also participate in maintaining application and infrastructure security.
Developers may be responsible for secure coding and addressing vulnerabilities identified during development, while operations teams can manage infrastructure security, access controls, and monitoring. This collaboration helps security become part of regular development and operational workflows rather than a task passed between teams.
4. DevSecOps Automatically Slows Down Software Delivery
Reality: Introducing security checks can add additional activities to a software delivery pipeline, particularly when a team is implementing DevSecOps practices for the first time. However, many of these checks can be automated and integrated into existing CI/CD workflows instead of being performed entirely through separate manual reviews.
The purpose is to identify security issues earlier, when they can be addressed as part of normal development work. The actual effect on delivery speed depends on factors such as the number of security controls, the level of automation, the application architecture, and how effectively the security processes are integrated into the pipeline.
5. DevSecOps Is Only Required for Regulated Industries
Reality: Compliance and regulatory requirements are common reasons for introducing DevSecOps, but they are not the only factors. Organisations outside highly regulated industries may also need stronger security practices when applications handle sensitive information, use cloud infrastructure, depend on third-party libraries, or have frequent release cycles.
DevSecOps can be applied at different levels depending on the risks and requirements of an organisation. A team may start with practices such as dependency scanning and secure coding checks and gradually introduce additional controls for infrastructure, access management, vulnerability monitoring, and security testing as its environment and requirements evolve.
Why and What Should You Choose: DevOps or DevSecOps?
If I were starting a software project today, I would choose DevSecOps from the beginning. I don’t see security as something that should be added after a team has already built its development and deployment process. If a team is already investing in automation, CI/CD, cloud infrastructure, and continuous delivery, leaving security outside that workflow creates an unnecessary gap.
That said, I don’t believe every organisation needs to immediately introduce a complicated security setup. For a small application with limited infrastructure and low-risk data, starting with strong DevOps practices and gradually introducing security controls can be a practical approach. But as soon as an application handles sensitive data, relies heavily on cloud infrastructure, uses third-party dependencies, or moves through frequent releases, I would strongly lean towards DevSecOps.
Why Would I Choose DevSecOps?
For me, the biggest reason is simple: security should be part of how software is built, not something checked after it has already been built. Finding a vulnerability during development gives a team the opportunity to fix it while the code, architecture, and context are still fresh. Finding the same issue after deployment can involve much more investigation, coordination, and disruption.
I also believe that DevSecOps fits naturally into the way modern development teams already work. If a team is automating builds, testing, deployments, and infrastructure, security checks can become part of those same workflows. Instead of asking developers to stop what they are doing for every security review, teams can automate appropriate checks and make security a regular part of the development process.
What Should You Choose?
My view is that the choice should be based on the risk and requirements of the application, not simply on whether an organisation calls itself “DevOps” or “DevSecOps.”
If the primary requirement is to improve collaboration between development and operations, automate repetitive processes, establish CI/CD, and create a more consistent software delivery workflow, DevOps can provide the foundation needed. However, if security is a significant concern — particularly for applications handling sensitive data, cloud environments, third-party dependencies, or frequent production releases — I would choose DevSecOps.
And if a team is already using DevOps, I would not recommend throwing away what is already working. I would build security into the existing pipeline step by step. In my opinion, that is the more practical way to approach DevSecOps: keep the DevOps foundation, bring security into it, and make security part of the team's everyday engineering process.
Conclusion
DevOps and DevSecOps are built around the same principles of collaboration, automation, continuous delivery, and shared responsibility, but they differ in how security fits into the development lifecycle. DevOps focuses on bringing development and operations together to improve software delivery, while DevSecOps takes that foundation further by making security part of the same process.
From my perspective, security should not be treated as a final checkpoint before deployment. If a team is already investing in automation and continuous delivery, integrating security into those workflows is a natural next step. Whether an organisation starts with DevOps or moves directly to DevSecOps, the important thing is to build a software delivery process where security, development, and operations work together rather than working in isolation.
Frequently Asked Questions

 WhatsApp
 Call Us
 Mail Us